First deployment | Audit & observability
Azul Trail Goes Live at the Ministry of Agriculture and Animal Resources, Rwanda
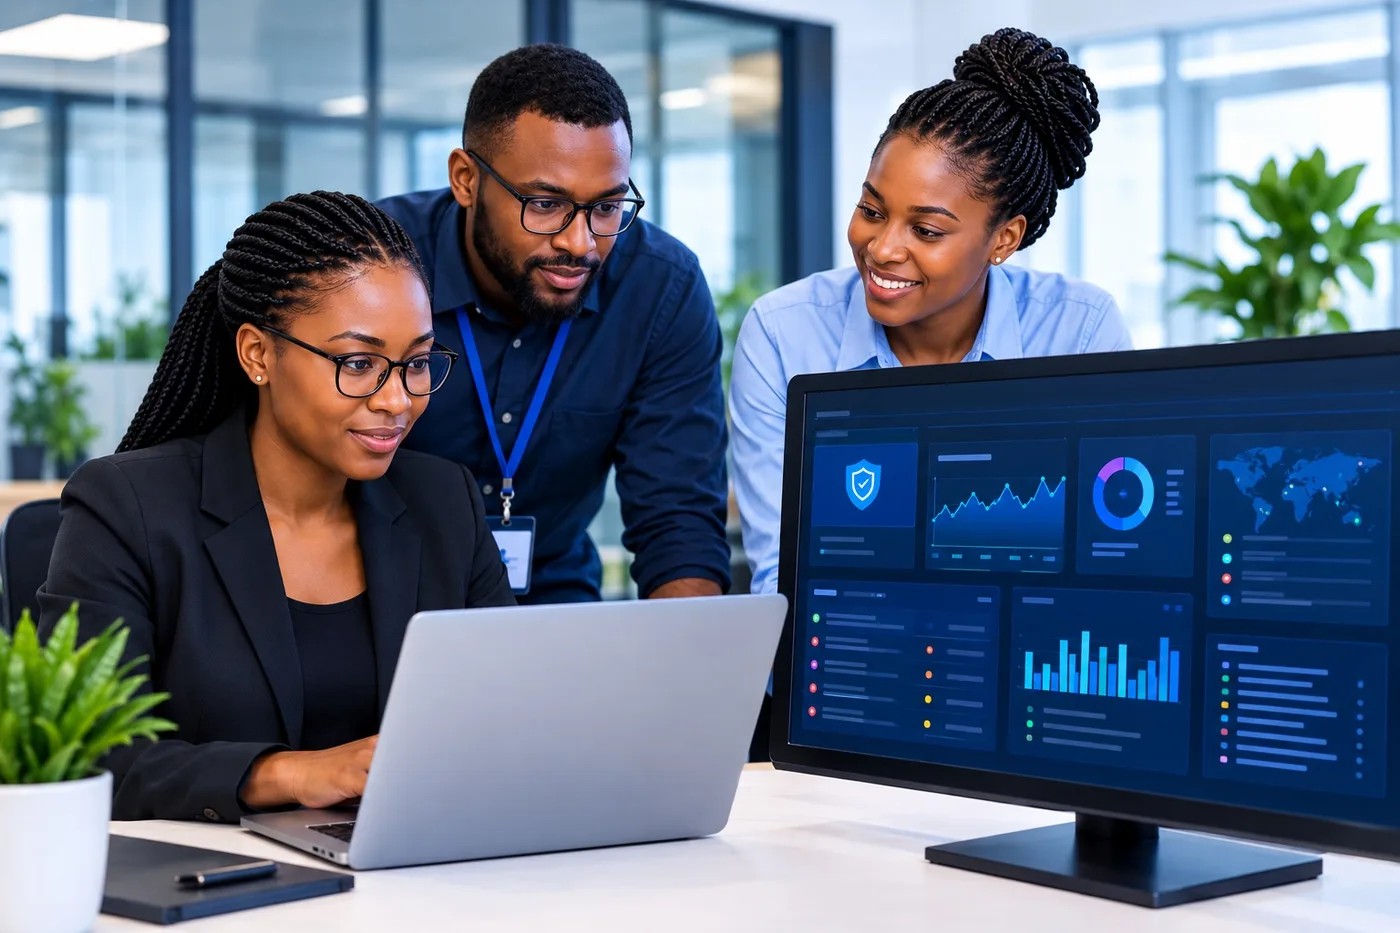
The first production deployment of Trail: real-time audit logging, a tamper-evident hash-chained record of every event, and OpenSearch-backed search across the ministry's systems.
- Milestone
- First production deployment
- Institution
- Ministry of Agriculture and Animal Resources, Rwanda
- Search engine
- OpenSearch
What happened
Trail is now running in production for the first time, at the Ministry of Agriculture and Animal Resources in Rwanda. Every security and operational event across the ministry's systems is captured as it happens and sealed into a record that cannot be quietly altered afterwards.
 Go furtherTrailLearn more
What it does
Trail captures logins, file downloads, and system activity in real time. Each entry carries a timestamp, a severity level, the entity affected, and the actor responsible, so a line in the log answers who did what, to what, and when.
It also tracks authentication activity and success rates, which is how a cluster of failed sign-ins stops being a statistic in a file nobody opens and becomes something a person is told about.
Alongside the audit trail, Trail indexes the institution's active documents into vector chunks, so staff can search the knowledge base by meaning rather than by exact keyword.
How it works
Every entry is hash-chained to the one before it. Each record carries a cryptographic fingerprint of its predecessor, so the log forms a chain rather than a pile. Altering a historic entry breaks every link after it, and the dashboard reports a verified chain only when the whole sequence still holds.
OpenSearch sits underneath for storage and querying, which is what makes investigation practical: fast search across the full history, system health checks, and JSON exports when an auditor wants the evidence in a form they can process themselves.
The problem it solves
Most institutions already keep logs. The difficulty is that those logs are trusted exactly as far as the administrator who can edit them, which means they answer the easy question and not the hard one. They can show what a well-behaved system did. They cannot prove what a compromised one did, because anyone able to cause the incident is usually able to edit the account of it.
For a ministry holding national agricultural data, that gap matters. Records inform subsidy decisions, food security planning, and the advice given to farmers. If the history of who changed what cannot be defended, neither can the decisions built on it.
The benefit day to day
For an administrator, a question that used to take a morning of grepping now takes a search box.
For a director, the audit pack an oversight body asks for is an export rather than a project.
For everyone using the systems, an unauthorised access attempt is noticed while it is still an attempt.